You work with sensitive data
The product stores personal or financial data, and access to it must be strictly limited.

A HashiCorp service for storing secrets centrally and managing access to them. We choose it when there are many systems and people and a leaked key is costly.

Database passwords and API keys often sit in configs, chats and spreadsheets for all to see. Vault gives access only to those who need it and logs every request, so leaks are easy to trace and close.
The product stores personal or financial data, and access to it must be strictly limited.
Passwords and keys are shared in messengers, and when someone leaves, no one knows what to change.
Partners, a regulator or internal policy require knowing who accessed which systems and when.
Services get database passwords and API keys from Vault at runtime, not from files in the code.
Dynamic accounts that are created on request and expire on their own.
Deployment pipelines take keys from Vault, so they are not stored in repository settings.
Vault encrypts sensitive fields, and the encryption keys never leave the vault.
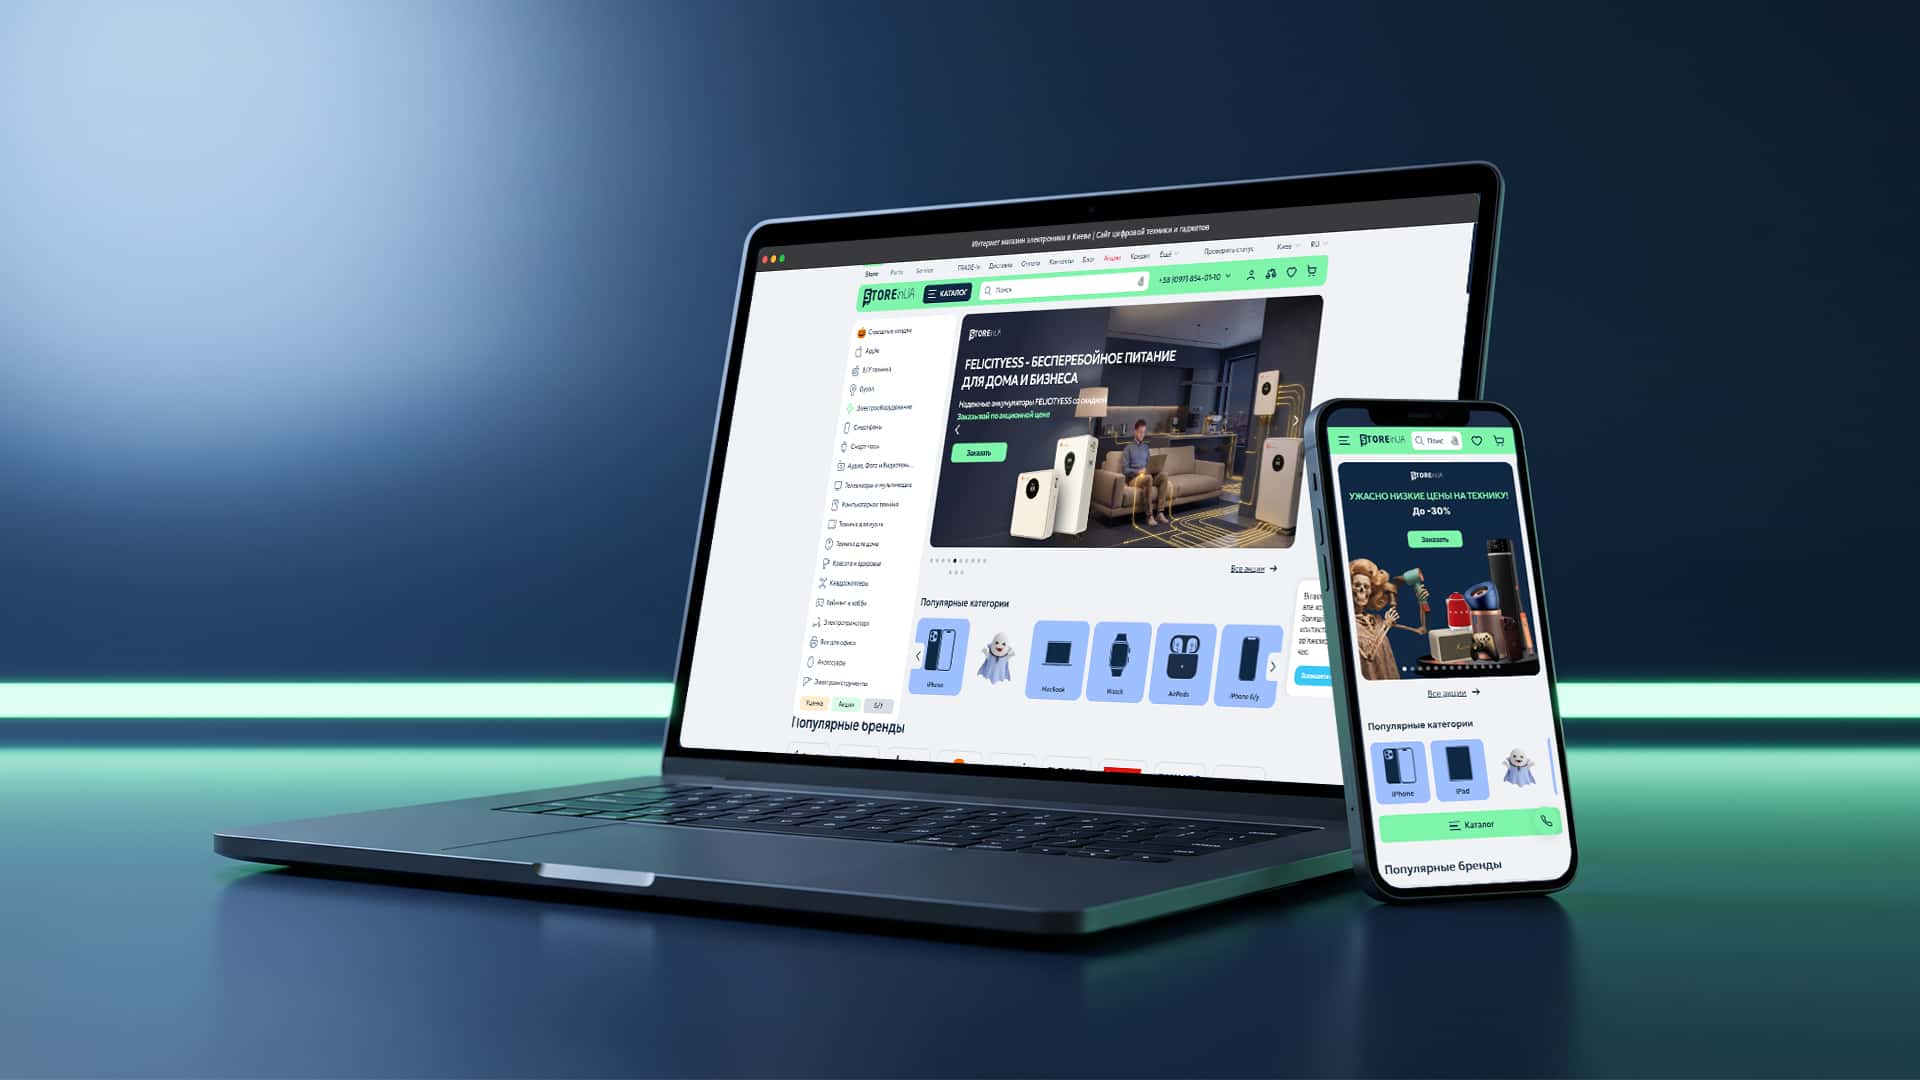 OCTOBER 2026eСommerce / DEVELOPMENT
Purchase conversion up from 1.4% to 3%: a new platform for 1M+ products with no sales stoppage.
Book a Clarity Session—a 30-minute review of your marketing. You will receive a map of bottlenecks and a clear understanding of the next steps.
Clarity first. Then — managed and systematic growth.
The team took a professional approach to upgrading site, ensuring high-quality project delivery without interrupting the store’s operations.
 Nikolay LuchinskyRetail Director / STOREinUA
It depends on your data and number of systems. With a few services and no sensitive information, the cloud's built-in secrets manager is enough. Vault pays off when there are many systems, access changes often or a full audit is required.
Secrets Manager is convenient if everything lives in AWS. Vault works the same in any cloud and on your own servers, and it can also issue temporary access and encrypt application data, so we choose it for mixed infrastructure.
Applications can't get new secrets, so we deploy Vault with redundancy and a well-planned recovery procedure. We describe and test these scenarios before launching in production.
Setting up HashiCorp Vault at GVSPACE means putting access in order: we move passwords, API keys and certificates out of configs and chats into a central store, and set up policies, temporary accounts and an audit log. We integrate Vault with applications, databases and CI/CD pipelines for products that handle personal and financial data and must meet partners' security requirements.