Nobody has owned security
The product was shipped fast: passwords sit in shared chats, former contractors still have access, and nobody has tested the backups.

We look for weaknesses in sites, apps and infrastructure. Risks to money and customer data are closed first.
The product was shipped fast: passwords sit in shared chats, former contractors still have access, and nobody has tested the backups.
Large clients and partners send security questionnaires, and the team cannot answer concretely about data and access.
There are so many servers, services and contractors that nobody sees the full map of access and entry points.
 [ 01 ]free · 30 min
We review where data lives, who has access, and what happens if a service goes down. You leave with the main risks. No sales pitch.
 [ 02 ]14 business days
We check applications, infrastructure and access. You get a report of vulnerabilities ranked by the damage to the business.
 [ 03 ]depends on scope
We close critical issues first, then the rest by plan. Each fix is confirmed with a retest.
 [ 04 ]ongoing, monthly cycle
We watch security events, update dependencies and review access regularly as the team grows.
and answers
They are different jobs. DevOps keeps the system stable and updating quickly. Cybersecurity keeps outsiders from using it. The practices overlap: access, secrets, updates. DevOps optimizes release speed, while a security audit looks for the holes that speed left behind. It works best when both are aligned.
No. Absolute protection does not exist, and anyone who promises it is misleading you. We lower the chance of an incident and limit the damage if one happens: known vulnerabilities closed, access restricted, monitoring in place and recovery from backups tested.
No, if it is planned properly. We agree the testing in advance: what we check, at what hours and on which environment. Risky checks run on a test copy, not on the live system with real customers.
Yes, and small companies often need it most. Most attacks are automated and look for typical mistakes, not famous brands. For a small company the audit is smaller, and one leak of the customer base can cost more than the whole protection effort.
Start with a free 30-minute Clarity Session.
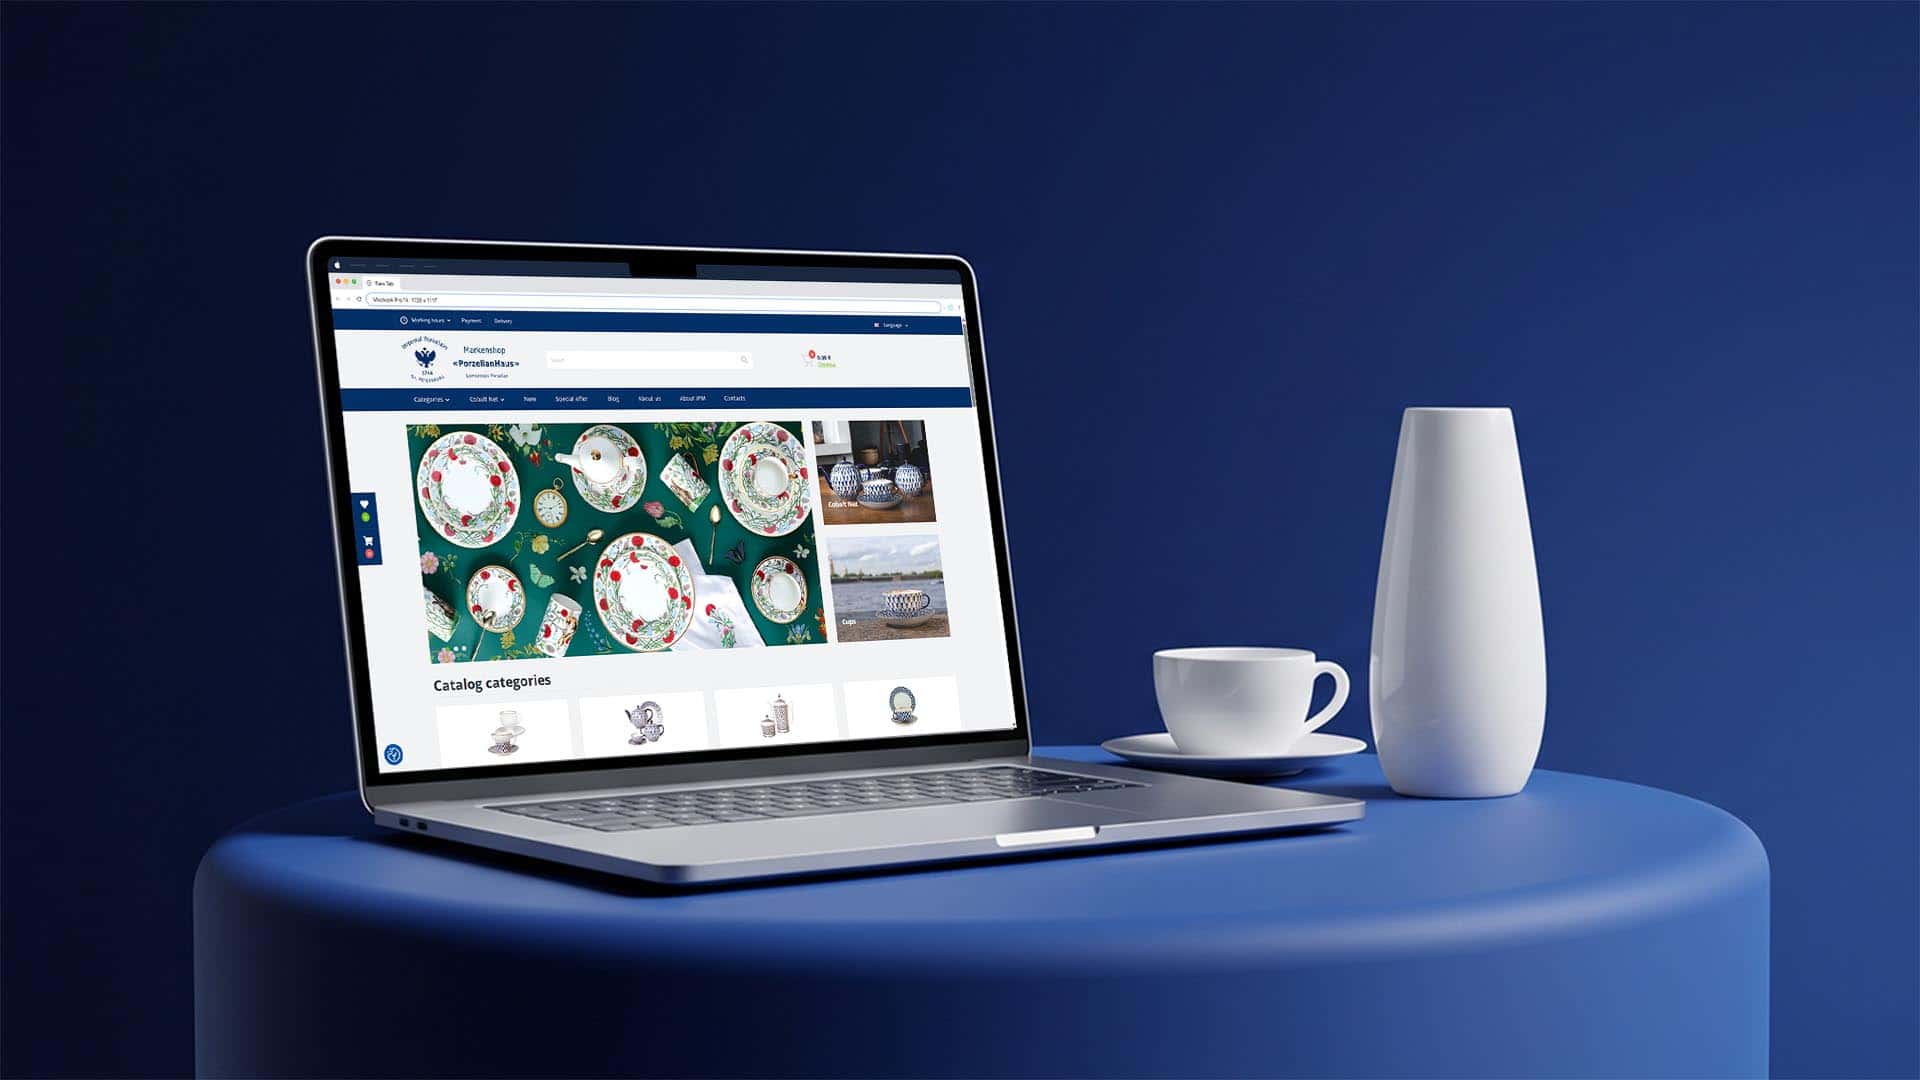 OCTOBER 2026eСommerce / SEO
Google visibility grew by 600% — up to 42 queries in the top 3.
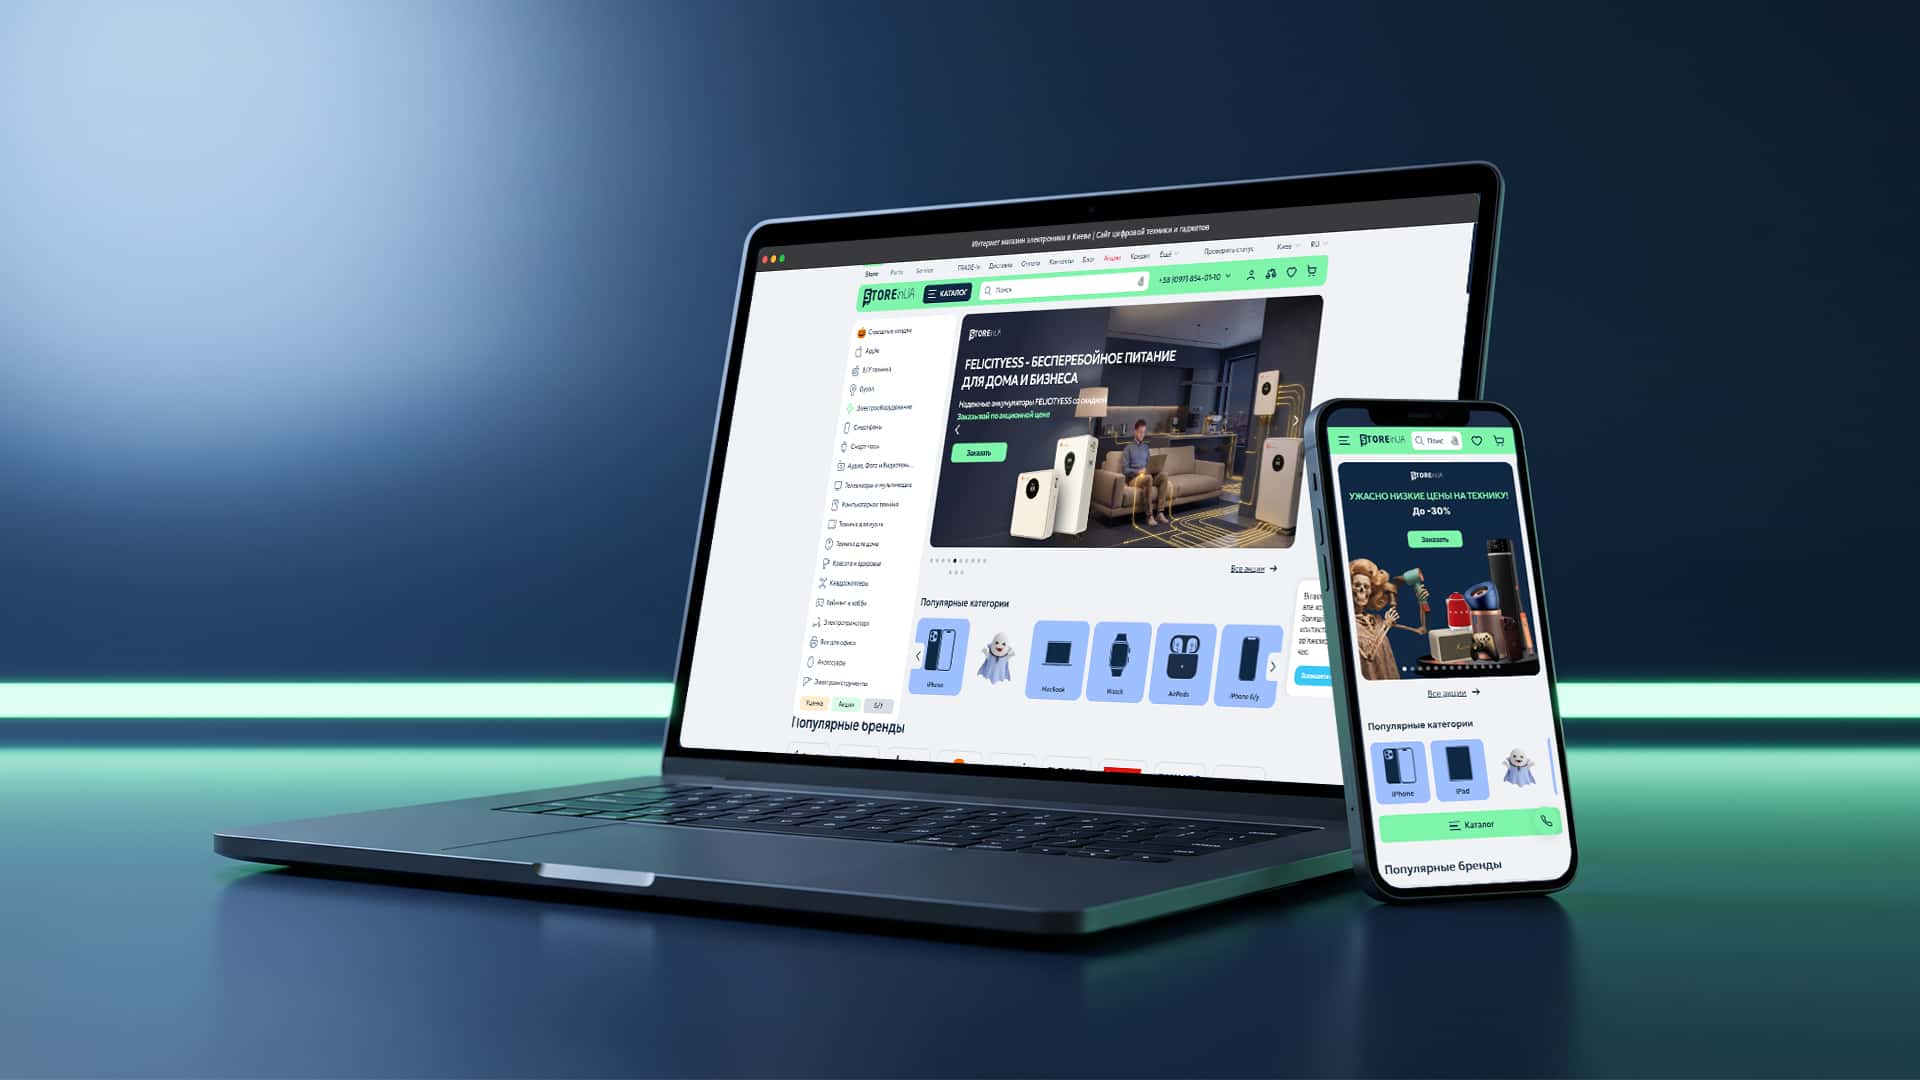 OCTOBER 2026eСommerce / DEVELOPMENT
Purchase conversion up from 1.4% to 3%: a new platform for 1M+ products with no sales stoppage.
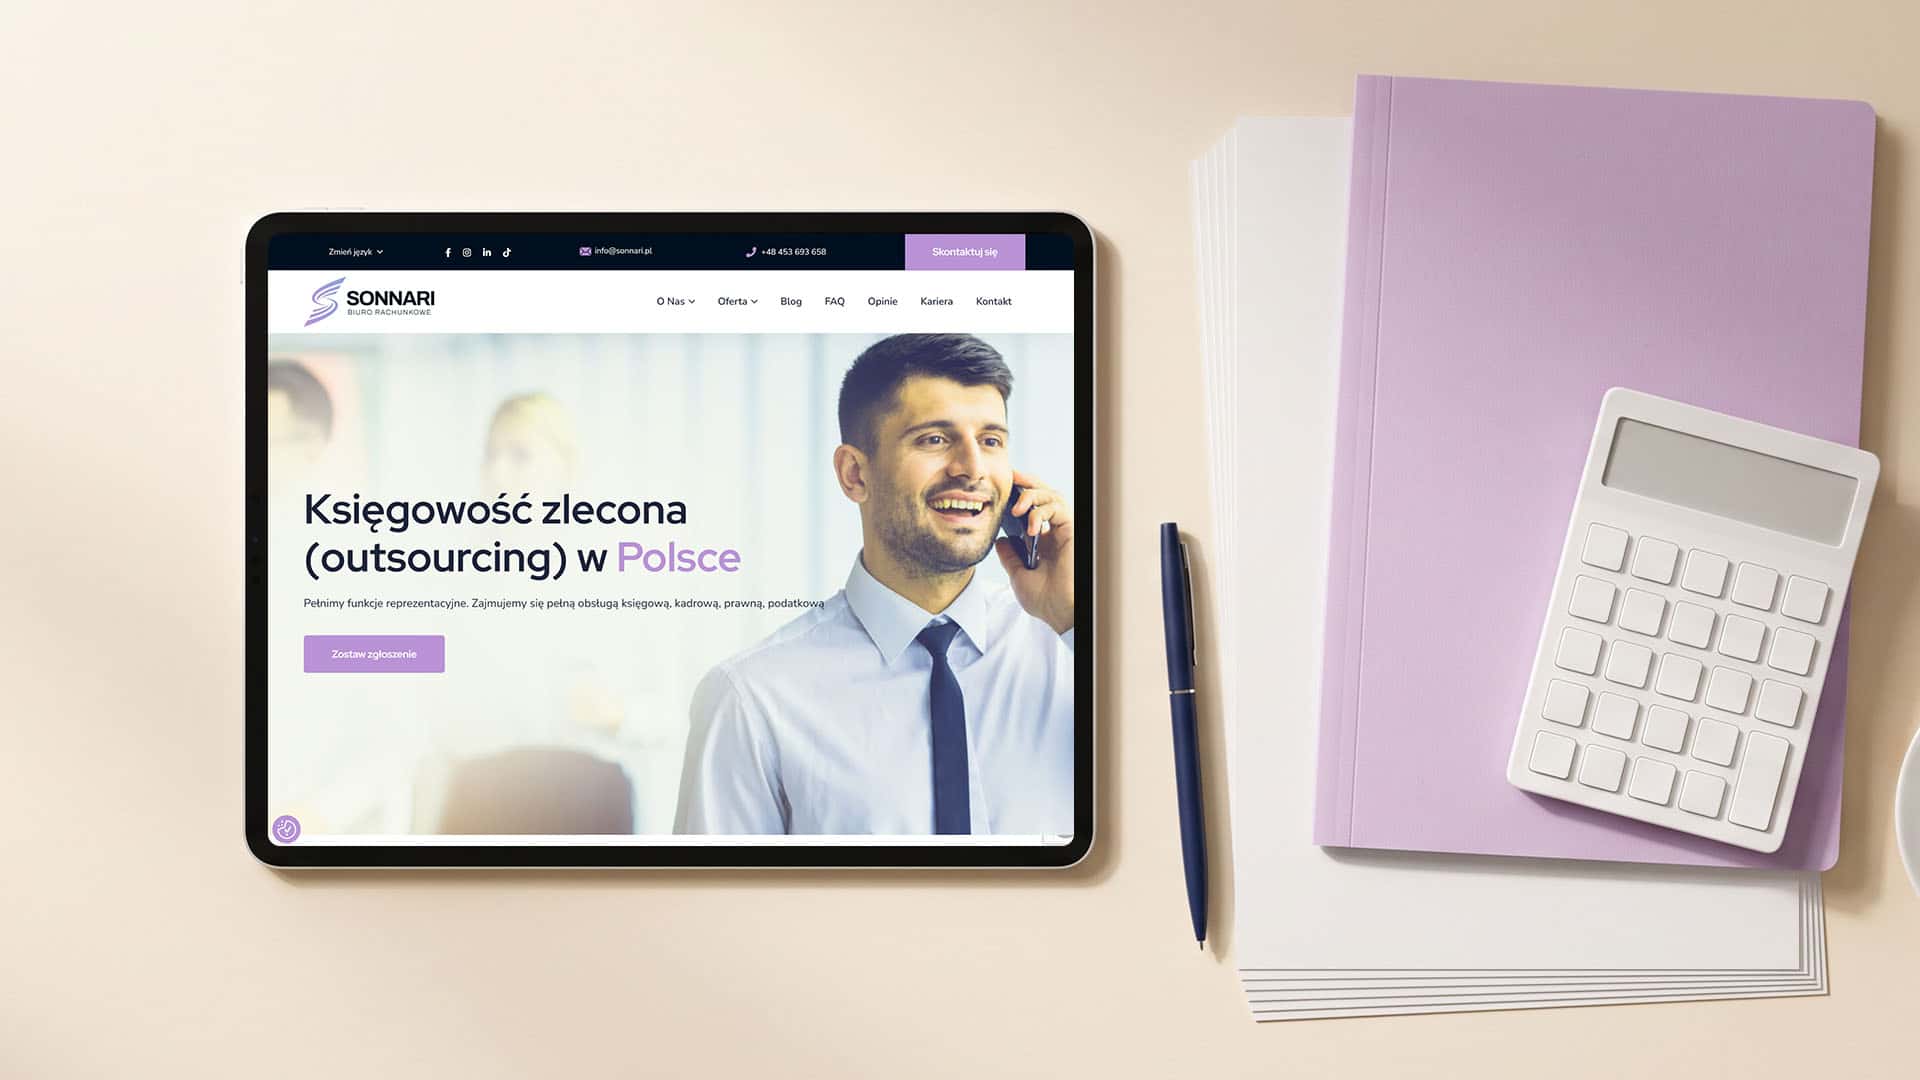 OCTOBER 2026SERVICES / MARKETING
Google visitors grew from 360 to 7000 per month, with 261 queries in the top 10: SEO for accounting in Poland.
Author: GVSPACE
Author: Vasyl Horaichuk
Author: GVSPACE